
Managed IT and cybersecurity for nonprofits in Maryland and DC.
EDG.tech runs IT and security for nonprofits across Gaithersburg, Rockville, Bethesda, Germantown, Washington, DC, and Frederick: donor and member data protected, staff and volunteer devices managed, the security documentation funders ask for, and a helpdesk that treats a six-person organization like a client. Essentials is $45 per device per month; Complete, with 24/7 monitoring, is $100 per user per month.
Who this is for
For nonprofits of roughly 4 to 60 staff: human services, associations, arts and education organizations, faith-based groups, and foundations, with or without a part-time IT volunteer. Organizations with a federal grant that carries specific security clauses, or that process health information, fit Complete; a large institution with its own IT department does not need us.
What is at stake for a nonprofit?
Most nonprofits have no security budget at all
In the CyberPeace Institute's 2023 survey of nonprofits, 56% had no budget allocated to cybersecurity and 70% did not believe they had the knowledge, skills, and resilience to respond to an attack. Attackers know the sector is cyber-poor and target-rich: donor lists, bank details, and a staff too busy to question an urgent email.
Source: CyberPeace Institute / Protect.ngo: Cyber-poor, target-rich (Mar 25, 2024; 2023 survey)
Grant and vendor payments are the money attackers go after
The FBI's Internet Crime Complaint Center recorded 24,768 business email compromise complaints and $3.05 billion in losses in 2025. For a nonprofit the version is an email that looks like the executive director asking finance to change a vendor's bank account, or a funder's payment redirected before it arrives.
Donor records are personal information under Maryland law
Maryland's Personal Information Protection Act requires any business, including a nonprofit, that holds personal information to maintain reasonable security procedures and to notify affected individuals within 45 days of discovering a breach. A donor database with names, addresses, and payment details is squarely inside it.
Source: Maryland Attorney General: PIPA guidelines for businesses
What do funders and Maryland law ask of a nonprofit?
There is no single nonprofit security regulation, which is why the obligations arrive from three directions. Maryland's Personal Information Protection Act covers donor, member, client, and employee records, with a reasonable-security duty and a 45-day breach notice. Funders increasingly ask about security in grant applications and audits, and federal awards can carry specific data-protection clauses. Organizations that take card payments answer to their payment processor's PCI requirements, and any that handle health information for program participants fall under HIPAA. Cyber-insurance carriers ask for multi-factor authentication, backups, and training before they quote a nonprofit at all. EDG.tech sets up the controls, writes the policy your board can adopt, and keeps the evidence organized so the next grant application or audit question has an answer.
How does EDG.tech serve nonprofits?
Donor and member data, locked to the people who need it
The donor database, the membership system, and the finance files get named accounts with multi-factor authentication instead of the shared login everyone knows, access scoped to role, and encrypted backups, so a departing employee or a lost laptop does not become a notice to every donor.
Grant-ready security documentation
A board-adoptable security policy, a list of the controls in place, an incident response plan, and training records, kept current and written in plain language, so when a funder's application asks how you protect data, development can answer in an afternoon instead of asking IT to invent something.
Staff, volunteers, and board on devices you can actually manage
Organization-owned laptops are enrolled, encrypted, and patched; personal devices used by volunteers and board members get a safe path to email and files without exposing the rest, and both can be cut off the same day someone leaves, which in a nonprofit is often the day after the gala.
Finance that cannot be talked into a wire
Email authentication on your domain, impersonation detection on messages that mention bank accounts or urgent payments, and a two-person verbal confirmation rule for any change to vendor or payroll banking, written with your finance committee and drilled with staff.
Which plan fits a nonprofit?
Smart, affordable IT management & cybersecurity.
See EDG.tech EssentialsMost small nonprofits start on Essentials: per-device pricing fits an organization where staff share workstations and the budget is approved by a board, and it delivers the managed devices, patching, backup, and core protection funders ask about. Complete fits organizations that handle health information, take card payments at scale, or hold a federal award with security clauses, because it adds the 24/7 security operations center and per-user protection of email and identities.
EDG.tech Complete is $100 per user per month. Compare both plans
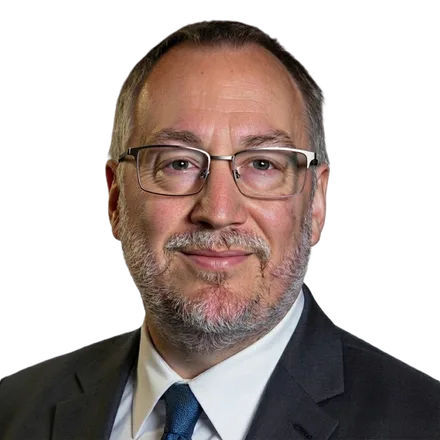
"Nonprofits run on trust and a tight budget, and attackers count on both. We give an organization enterprise controls at a price a board will approve, and the paperwork to prove it to a funder," says Duane Epperly, founder of EDG.tech.
“As the Executive Director of a small nonprofit, having a trusted technology partner is essential. Choosing EDG.Tech was absolutely the right decision. Their team is approachable, responsive, and consistently provides outstanding support. No matter the size of the issue, they treat every request as a priority.”
Nonprofit IT questions, answered
What does managed IT cost for a small nonprofit?
EDG.tech Essentials is $45 per device per month, month to month with no long-term contract, and covers monitoring, patching, backup, core protection, helpdesk, and a Success Coach. A nonprofit with 12 computers pays $540 per month. Complete, at $100 per user per month, adds 24/7 security monitoring and email and identity protection for organizations with higher-risk data.
Do you offer a nonprofit discount?
Our published prices are already set for small organizations, and we do not run a separate nonprofit rate card. What we do is help you use the discounted and donated software licensing programs available to registered nonprofits, which often saves more than a discount on our fee would, and we size the plan so you pay for the devices and people you actually have.
Can you help us answer security questions on grant applications?
Yes. We maintain a plain-language summary of your controls, a board-adopted security policy, and an incident response plan, and we answer the technical questions in funder applications, due-diligence questionnaires, and audits with you. Organizations on either plan get this documentation as part of onboarding.
Our staff and volunteers use their own laptops. Can you still protect us?
Yes. Organization-owned devices are fully managed, and personal devices get a secure path to email and files with multi-factor authentication and the ability to remove access remotely, without us managing the whole device. We will also tell you which roles, usually finance and development, should be on organization-owned, managed equipment.
Sources
- CyberPeace Institute / Protect.ngo: Cyber-poor, target-rich (Mar 25, 2024; 2023 survey)
- FBI IC3 2025 Internet Crime Report (PDF)
- Maryland Attorney General: PIPA guidelines for businesses
- Md. Code, Com. Law § 14-3504 (breach notice, 45 days)
- HHS: HIPAA Security Rule (for nonprofits handling health information)
Last reviewed: October 10, 2026
Ready for IT you never have to worry about?
Book a free 30-minute consultation, or start with a free security assessment. You get a fixed price within two business days. No pressure, no jargon.