
Managed IT and cybersecurity for Maryland financial firms.
EDG.tech runs IT and security for independent advisors, CPA and tax firms, bookkeepers, and mortgage brokers across Gaithersburg, Rockville, Bethesda, Germantown, Washington, DC, and Frederick: the written security program the FTC Safeguards Rule requires, multi-factor authentication on every client-data login, encrypted document exchange, and 24/7 monitoring. Complete is $100 per user per month; Essentials is $45 per device per month.
Who this is for
For independent registered investment advisers, CPA and tax practices, bookkeeping firms, and mortgage brokers of roughly 3 to 75 people. Banks and credit unions have examiners and requirements of their own, and broker-dealers with a home-office compliance department usually have IT dictated to them; we are the right fit when you are responsible for your own program.
What is at stake for a financial firm?
A breach of 500 clients is now a federal report, inside 30 days
Since May 13, 2024, non-bank financial institutions under FTC jurisdiction, which includes investment advisers, tax preparers, and mortgage brokers, must notify the FTC of a security breach involving the information of at least 500 consumers no later than 30 days after discovery. The report is public. The clock runs whether or not you have an incident response plan.
Source: FTC: Safeguards Rule notification requirement now in effect (May 14, 2024)
Tax and accounting professionals are required by law to have a written security plan
The IRS and its Security Summit partners restated it in August 2026: federal law requires tax and accounting professionals to create and maintain a Written Information Security Plan. The IRS publishes a template, Publication 5708, and expects the plan to be real, reviewed, and specific to the practice. A plan that exists only as a downloaded PDF is the thing examiners find first.
Source: IRS: tax pros need a Written Information Security Plan (Aug 18, 2026, IR-2026-92)
Your clients are the target, and your name is the bait
The FBI's Internet Crime Complaint Center recorded 72,984 investment fraud complaints and $8.65 billion in losses in 2025, the largest category by dollars, and $3.52 billion of it came from victims over 60. A spoofed email from an advisor or accountant is how many of those start, which makes your domain's email authentication part of your clients' protection.
What do the FTC Safeguards Rule and the IRS ask of a financial firm?
The FTC Safeguards Rule (16 CFR Part 314) applies to non-bank financial institutions, including registered investment advisers not regulated by the SEC's own rules, tax preparers, bookkeepers, and mortgage brokers. It requires a written information security program with a designated qualified individual, a risk assessment, access controls, encryption, multi-factor authentication, secure disposal, vendor oversight, staff training, an incident response plan, and, since 2024, notice to the FTC within 30 days of a breach affecting 500 or more consumers. The IRS requires tax professionals to maintain a Written Information Security Plan and publishes the template in Publication 5708. SEC-registered advisers answer to Regulation S-P instead, which added its own incident response and 30-day notice duties. Maryland's Personal Information Protection Act and your cyber-insurance carrier add their own asks. EDG.tech writes the program, runs the controls, and produces the annual report.
How does EDG.tech serve financial firms?
The written program, kept alive
We draft your information security program and WISP from your actual systems rather than a template, name the controls behind each requirement, and refresh it on a schedule, so the risk assessment, vendor list, training log, and annual report to leadership are current when an examiner, a carrier, or a custodian asks.
Client data moves through one encrypted door
Tax documents, statements, and account applications travel through an encrypted client portal rather than email attachments, with multi-factor authentication on the portal, the tax and planning software, and the custodian and lender logins, and access removed the same day a preparer or associate leaves.
Tax season and quarter-end without a help ticket
Capacity planning before the January rush, spare hardware staged for the inevitable failure the week of a deadline, remote access that works from the kitchen table at 11 PM, and a helpdesk that treats a locked-out preparer on April 10 as the emergency it is.
Protecting clients from the firm's own name
Email authentication so no one can send mail as your domain, lookalike-domain monitoring, impersonation detection on anything that mentions wiring, distributions, or account changes, and a verbal confirmation policy for money movement that we write with you and train your staff on.
Which plan fits a financial firm?
Enterprise-grade managed IT & cybersecurity, fully managed, 24/7.
See EDG.tech CompleteFinancial firms belong on Complete. The Safeguards Rule and the IRS both expect monitoring, multi-factor authentication, encryption, and training for everyone who touches client data, and Complete's per-user pricing covers each person's devices, logins, and mailbox together with the 24/7 security operations center that detects a compromised account. Essentials fits a one- or two-person tax office with a short season and a small device count.
EDG.tech Essentials is $45 per device per month. Compare both plans
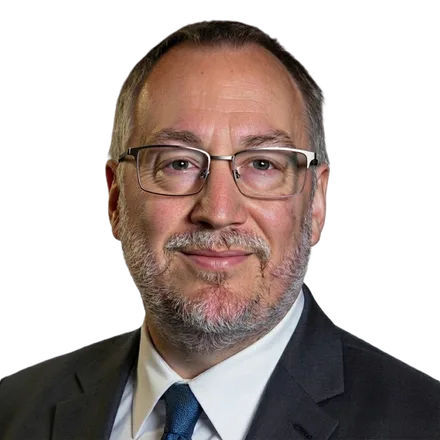
"The Safeguards Rule does not care how big your firm is. It cares whether the plan you wrote matches what is actually running on your computers. We make the two the same thing," says Duane Epperly, founder of EDG.tech.
Financial firm IT questions, answered
Does the FTC Safeguards Rule apply to a small advisory or tax practice?
Yes, if you are a non-bank financial institution under FTC jurisdiction, which covers most state-registered investment advisers, tax preparers, bookkeepers, and mortgage brokers regardless of size. Firms that keep information on fewer than 5,000 consumers are exempt from a few written-program elements, but the core safeguards and the 30-day breach notice still apply. SEC-registered advisers follow Regulation S-P instead.
Can EDG.tech write our WISP?
Yes. We write the Written Information Security Plan from your real systems, following the structure in IRS Publication 5708, and we name the technical controls behind each section so the document and the network match. You review and adopt it, we maintain it inside the plan, and it is ready to hand over when the IRS, a carrier, or a custodian asks.
What does managed IT cost for a financial firm?
EDG.tech Complete is $100 per user per month and includes the controls the Safeguards Rule expects: encryption, multi-factor authentication, patching, backup, training, and 24/7 monitoring. An eight-person advisory firm pays $800 per month. The initial written program and risk assessment are a project quoted per client environment, then maintained in the plan.
How do you protect our clients from wire and distribution fraud?
Three layers: email authentication so nobody can send mail as your domain, impersonation detection on messages about wiring or account changes, and a verbal confirmation policy for any money movement request, written with you and drilled with staff. We also monitor for lookalike domains registered to imitate your firm.
Will you work with our custodian, tax software, and planning tools?
Yes. We support the custodian portals, tax preparation, bookkeeping, planning, and document management tools you already use, manage the logins and multi-factor authentication around them, and coordinate with each vendor's support when a problem is on their side. We do not resell any of it, so our advice carries no commission.
Sources
- FTC: Safeguards Rule notification requirement now in effect (May 14, 2024)
- FTC: Safeguards Rule, what your business needs to know
- 16 CFR Part 314 (eCFR)
- IRS: tax pros need a Written Information Security Plan (Aug 18, 2026, IR-2026-92)
- IRS Publication 5708 (Rev. 8-2024): Creating a WISP
- IRS Publication 4557: Safeguarding Taxpayer Data
- SEC: Regulation S-P amendments (May 16, 2024, release 2024-58)
- FBI IC3 2025 Internet Crime Report (PDF)
- Maryland Attorney General: PIPA guidelines for businesses
Last reviewed: October 10, 2026
Ready for IT you never have to worry about?
Book a free 30-minute consultation, or start with a free security assessment. You get a fixed price within two business days. No pressure, no jargon.